STORM Platform · Threat Intelligence

Turn external signals into usable context.

Explore emerging vulnerabilities, publicly disclosed breaches and supplier-related threat signals in one workspace—then use that visibility to support risk assessment and remediation decisions.

STORM currently supports periodically synchronised vulnerability and breach intelligence, with filtering by supplier, vendor, severity and geography.

Threat landscapeSignals connected
Vulnerability signalSeverity, CVSS, vendor and product
Disclosed breachIncident and geographic context
Supplier signalBreach and vendor exposure
CVE ExplorerSearch, filter and review synchronized vulnerability records.
Breach viewMonitor publicly disclosed security incidents.
Supplier signalsTrack third-party breaches and vendor-specific vulnerabilities.
Periodic syncRefresh public threat-intelligence feeds on a periodic basis.
From volume to relevance

Explore the signal before it becomes a blind spot.

Public vulnerability and breach feeds generate more information than teams can use without a way to search, filter and place it in context. STORM centralizes those records and adds supplier, vendor, severity and geographic perspectives so security teams can investigate what deserves attention.

01 · MONITOR

See the landscape

Use a centralized dashboard for vulnerability trends, severity distribution and key metrics.

02 · EXPLORE

Investigate CVEs

Search vulnerability details and narrow results by date, severity, vendor and more.

03 · WATCH

Track third parties

Monitor supplier breaches and vulnerabilities associated with specific vendors.

04 · INFORM

Support decisions

Use relevant intelligence to inform risk assessment and remediation activity.

Inside the platform

A searchable view of the evolving threat landscape.

The module combines dashboard visibility, detailed vulnerability exploration and breach intelligence without presenting every external signal as an internal finding.

01 · Central dashboard

See trends, severity and recent signals together.

Bring periodically synchronized CVE data and disclosed breach intelligence into a single dashboard. Review vulnerability volumes, severity distribution, recent records and trend metrics before moving into detailed investigation.
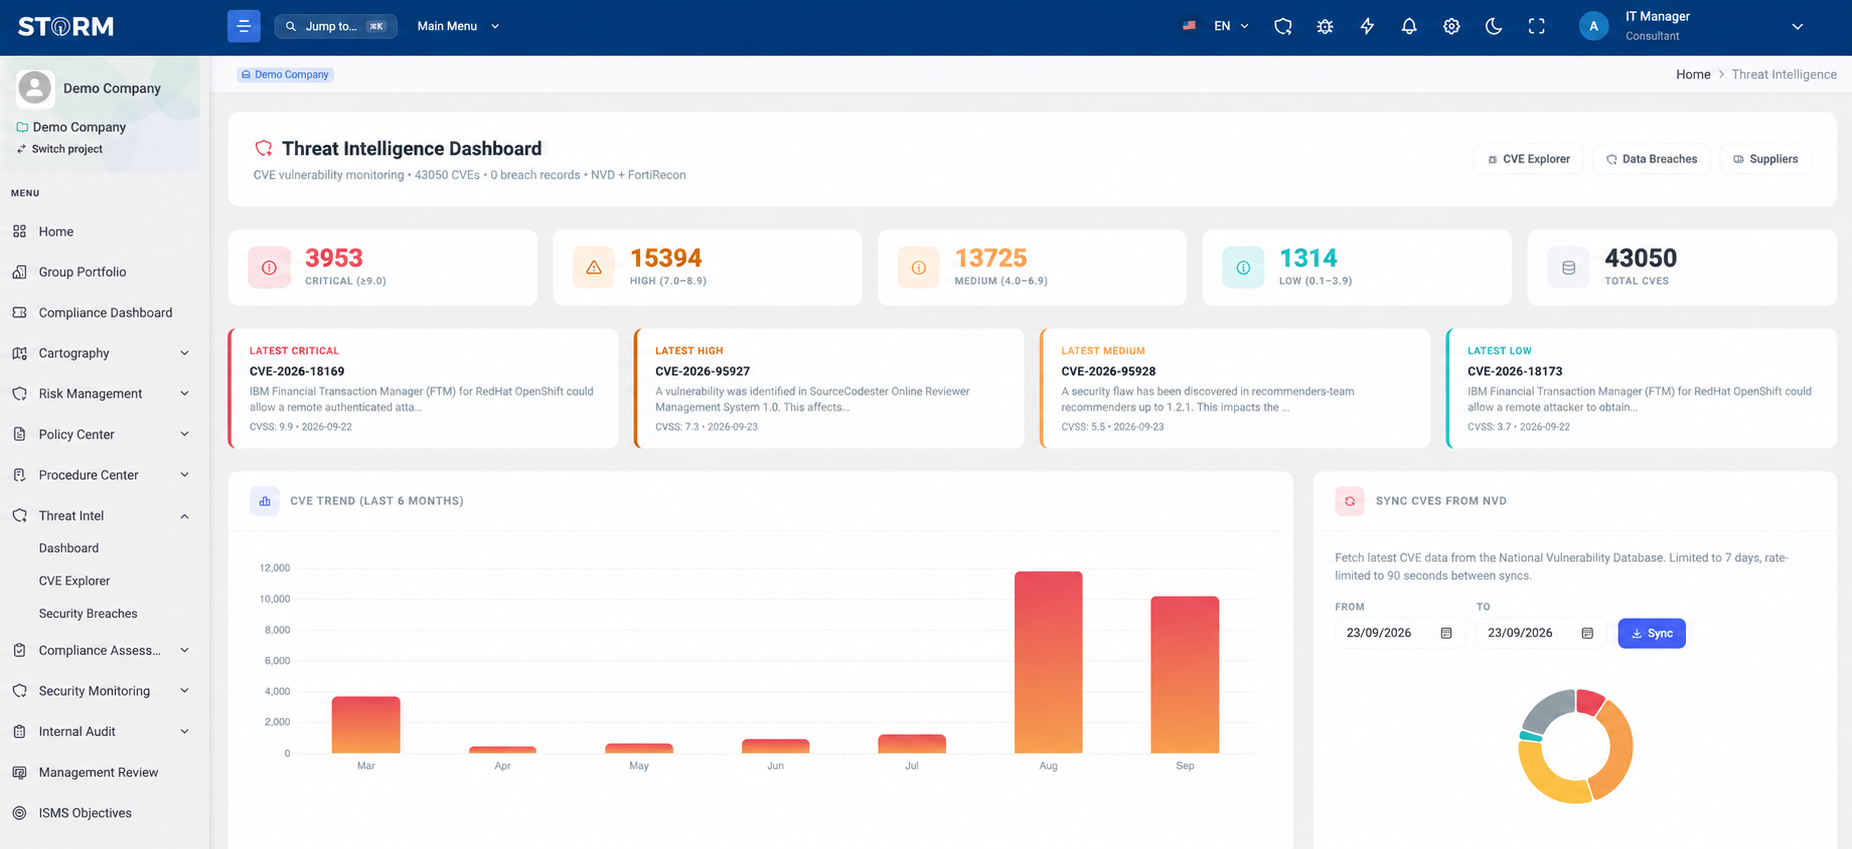
  • Current threat-landscape overview
  • Vulnerability trends and severity distribution
  • Key metrics with paths into CVEs, breaches and suppliers
STORM Threat Intelligence dashboard showing CVE severity, trends and breach navigation
02 · CVE Explorer

Filter vulnerability intelligence down to what matters.

Search and review CVE details, then filter by publication date, severity, CVSS score, vendor, product and other available attributes. The result is an investigation view, not a claim that every published CVE affects the organization.

  • Searchable CVE records
  • Date, severity and CVSS filtering
  • Vendor and product perspectives
SeverityCVSSVendorProductPublished
CVE recordVendor · Product · Published date · CVSS details
Critical
CVE recordSearchable vulnerability information and attributes
High
CVE recordReview details before determining organizational relevance
Review
CVE Explorer modelBuilt into STORM
03 · Breach and supplier monitoring

Watch beyond the organization’s perimeter.

Review publicly disclosed incidents, identify breaches relevant to the organization or its region, and monitor supplier-related security incidents and vendor-specific vulnerabilities.

  • Publicly disclosed breach intelligence
  • Supplier and third-party security incidents
  • Geographic breach filtering
Organization relevanceDisclosed incidents that may warrant investigation
Breach
Supplier monitoringThird-party breaches and vendor exposure
Supplier
Geographic contextFiltering for incidents and breaches by region
Region
Breach intelligence modelBuilt into STORM
04 · FortiRecon intelligence

Add external exposure and supply-chain signals.

The FortiRecon integration retrieves external threat and breach intelligence—including dark-web exposure, leaked credentials and vendor or supply-chain risk signals—for use in Threat Intelligence and Third-Party Risk Management.

  • Dark-web exposure signals
  • Leaked-credential intelligence
  • Vendor and supply-chain risk context
FortiReconExternal threat and breach intelligence
Source
Threat IntelligenceDisclosed breach information and external signals
Explore
Third-Party Risk ManagementSupplier evaluation and scoring context
Inform
FortiRecon integrationBuilt into STORM
From feed to decision

Keep intelligence exploratory, filtered and actionable.

The module supports investigation and informed remediation; response actions stay with your team.

01

Synchronize

Periodic public-feed updates

02

Explore

CVE and breach records

03

Filter

Severity, vendor, product and date

04

Relate

Supplier and geographic context

05

Inform

Risk and remediation decisions

Scope and delivery

What Threat Intelligence includes.

Threat-intelligence usefulness depends on feed scope, synchronization frequency and how signals move into the organization’s operational process.

Included in STORM

  • Public threat-intelligence feeds with CVE and breach records
  • CVE retrieval, periodic synchronization and detailed exploration
  • Date, severity, CVSS, vendor and product filtering
  • Supplier breaches and vendor-specific vulnerability monitoring
  • Geographic incident filtering
  • Vulnerability trends, severity distribution and key metrics
  • FortiRecon dark-web, leaked-credential and supply-chain signals

Good to know

  • Feed sources and synchronisation interval agreed at onboarding
  • Feeds synchronise periodically, not in real time
  • Automatic creation of internal findings, risks or tickets
  • FortiRecon licence arranged separately
Practical questions

Test the signals against what your team must investigate.

Bring the vendors, suppliers, products and geographies that define relevance for your organization.

What information does STORM Threat Intelligence aggregate?
Publicly available threat-intelligence feeds, including CVEs and breach intelligence, plus supplier-related incidents, vendor-specific vulnerabilities and FortiRecon external-exposure signals.
Are threat feeds synchronized in real time?
The documentation states that threat-intelligence feeds are synchronized periodically. It does not promise continuous real-time streaming or a guaranteed update interval, so timing should be confirmed for the intended deployment.
How can CVEs be filtered?
Filters include publication date, severity, CVSS score, vendor, product and other available attributes. The CVE Explorer also supports searching and reviewing vulnerability details.
Can STORM monitor supplier threats?
Yes. STORM monitors security breaches affecting suppliers and third parties, vendor-specific vulnerabilities, and FortiRecon vendor or supply-chain risk signals.
Can incidents be filtered by geography?
Yes. Security incidents and breaches can be filtered by geography, so teams can focus on the regions that matter to them.
Does Threat Intelligence automatically remediate threats?
No. Threat Intelligence provides visibility to support informed risk assessment and timely remediation; blocking and containment stay in your security tools.
How is this different from Technical Vulnerability Management?
Threat Intelligence explores external vulnerability and breach information. The separate Technical Vulnerability Management module centralizes findings from sources such as Nessus and Microsoft Defender and manages prioritization, remediation and SLA-driven workflows against organizational assets.

Bring the suppliers and products your team watches today.

Validate the feed scope, filters, FortiRecon signals and investigation workflow against the external exposure questions that matter to your organization.

Book a STORM demo
Certifications

ICT PROTECT, the company behind STORM GRC, holds internationally recognised certifications and independent assurance.

View all certifications
  • CERTIFIED ISO 27001
  • CERTIFIED ISO 22301
  • CERTIFIED ISO 9001
  • CERTIFIED CYBER ESSENTIALS
  • CERTIFIED CYBER ESSENTIALS PLUS
  • ASSURANCE ISAE 3000 TYPE II

The certifications and assurance reports shown here are held by ICT PROTECT and apply within their stated scope, which includes the STORM GRC platform.