Define scope and roles
Understand relevant privacy issues, interested parties, PII processing roles and PIMS boundaries.
Connect privacy scope, records of processing, DPIAs, controller and processor responsibilities, policies, risks, evidence, audits and improvement in one governed workspace.
STORM currently supports ISO/IEC 27701 privacy information management alongside ISO/IEC 27001 and GDPR.
ISO/IEC 27701:2025 defines requirements for establishing, implementing, maintaining and continually improving a PIMS. It can stand alone while remaining aligned with ISO/IEC 27001.
Understand relevant privacy issues, interested parties, PII processing roles and PIMS boundaries.
Establish privacy policy, accountability and responsibilities supported by management commitment.
Evaluate risks and opportunities, establish objectives and plan controlled changes.
Manage resources, competence, awareness, communication and controlled documented information.
Operate the processes and safeguards selected for the organisation's controller or processor activities.
Monitor relevant measures, conduct internal audits and document management review.
Address nonconformities, corrective actions and continual improvement of privacy management.
Operate the PIMS independently or align it structurally with an existing ISO/IEC 27001 system.
Built-in ISO/IEC 27701 assessments connect your PIMS to ROPA, DPIA, risks, policies and evidence.
STORM links processing context, privacy impact, provider oversight, controlled documentation, risk decisions and review records in a common operating environment.
Build records of processing and data maps alongside services, systems, users, locations, information assets and external providers.
ROPA · data mapping · CartographyUse the DPIA workflow and questionnaires to evaluate impact on data subjects and retain downloadable assessment records.
DPIA · impact evidenceManage policies and procedures through authoring, versions, approvals, reviews, acknowledgements, reminders and mappings.
Policy Center · lifecycleRecord likelihood, impact, controls, treatment decisions, mitigation actions, owners, dates and supporting attachments.
Risk Registry · treatmentMaintain supplier records, apply configurable assessment criteria, request evidence and track remediation and monitoring.
TPRM · supplier evidenceBring assessment status, findings, risks, incidents, supplier results, policy status and actions into structured reviews.
Audit · management review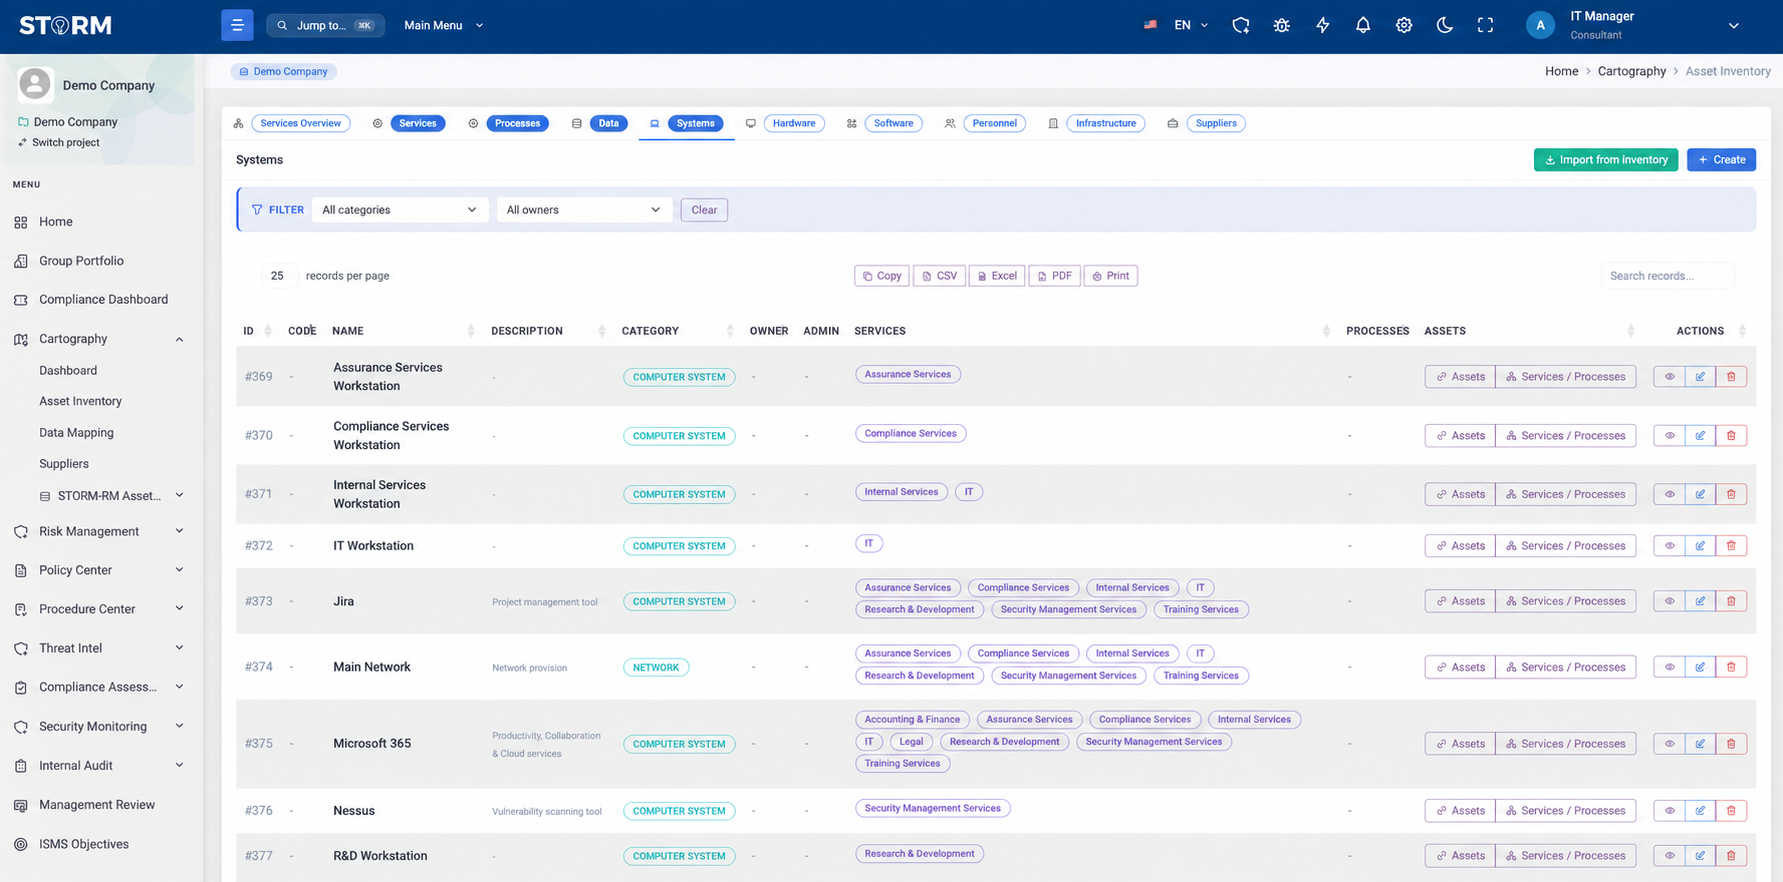
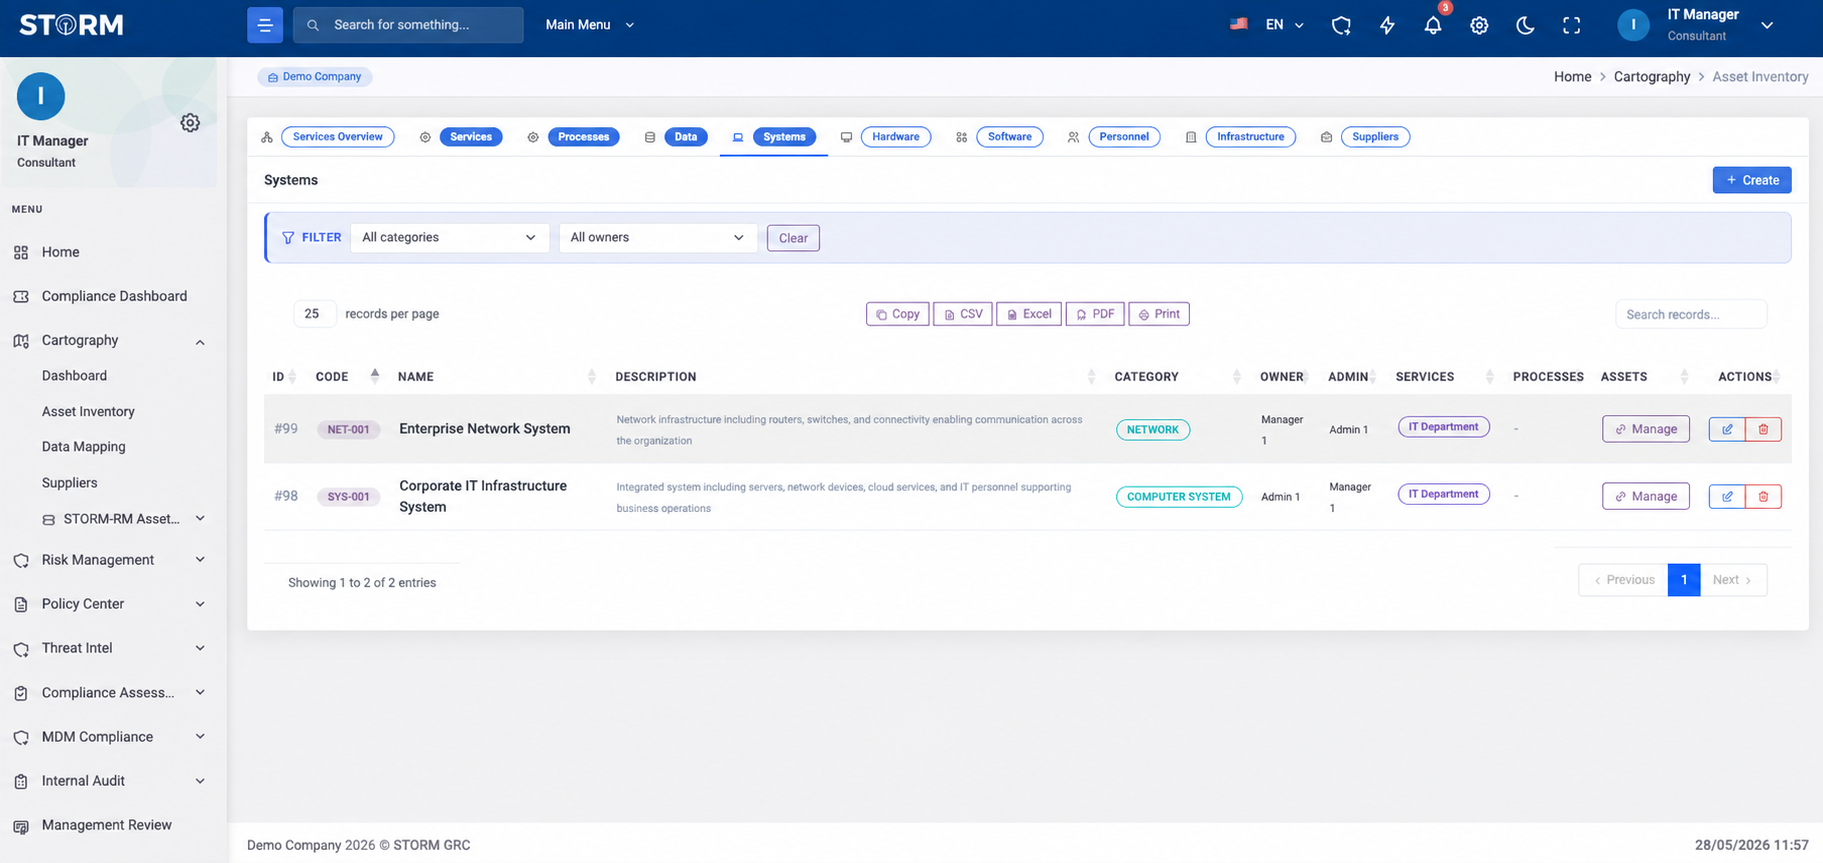
STORM supports ROPA and GDPR data mapping within a connected asset model. That makes privacy scope easier to relate to services, systems, people, locations and suppliers.
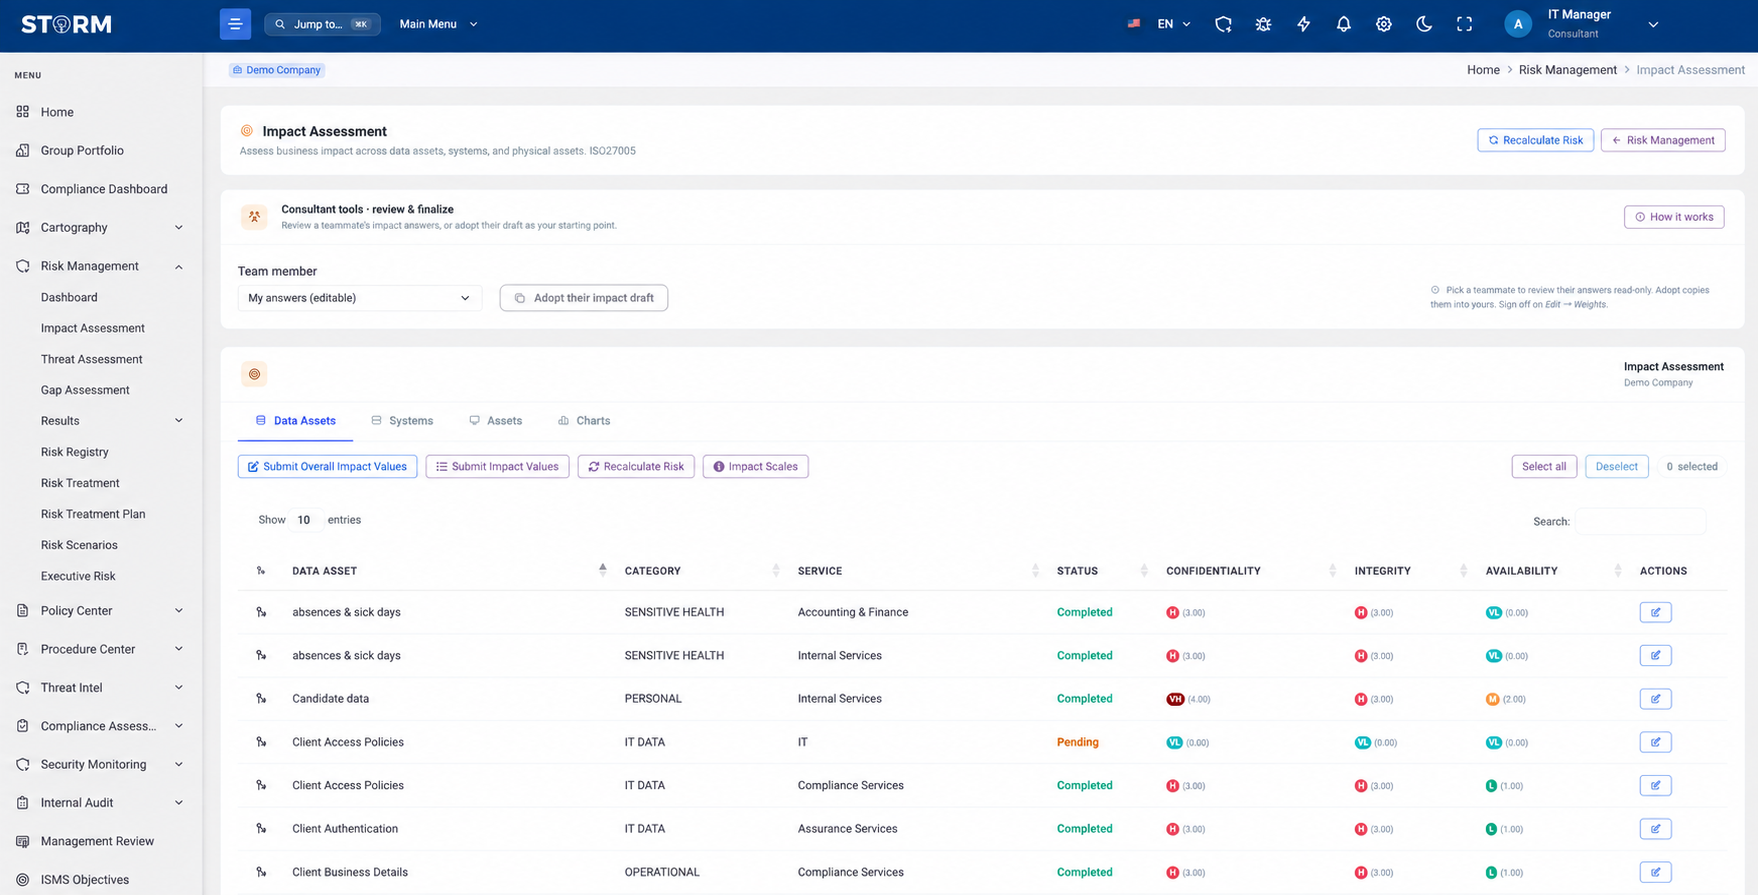
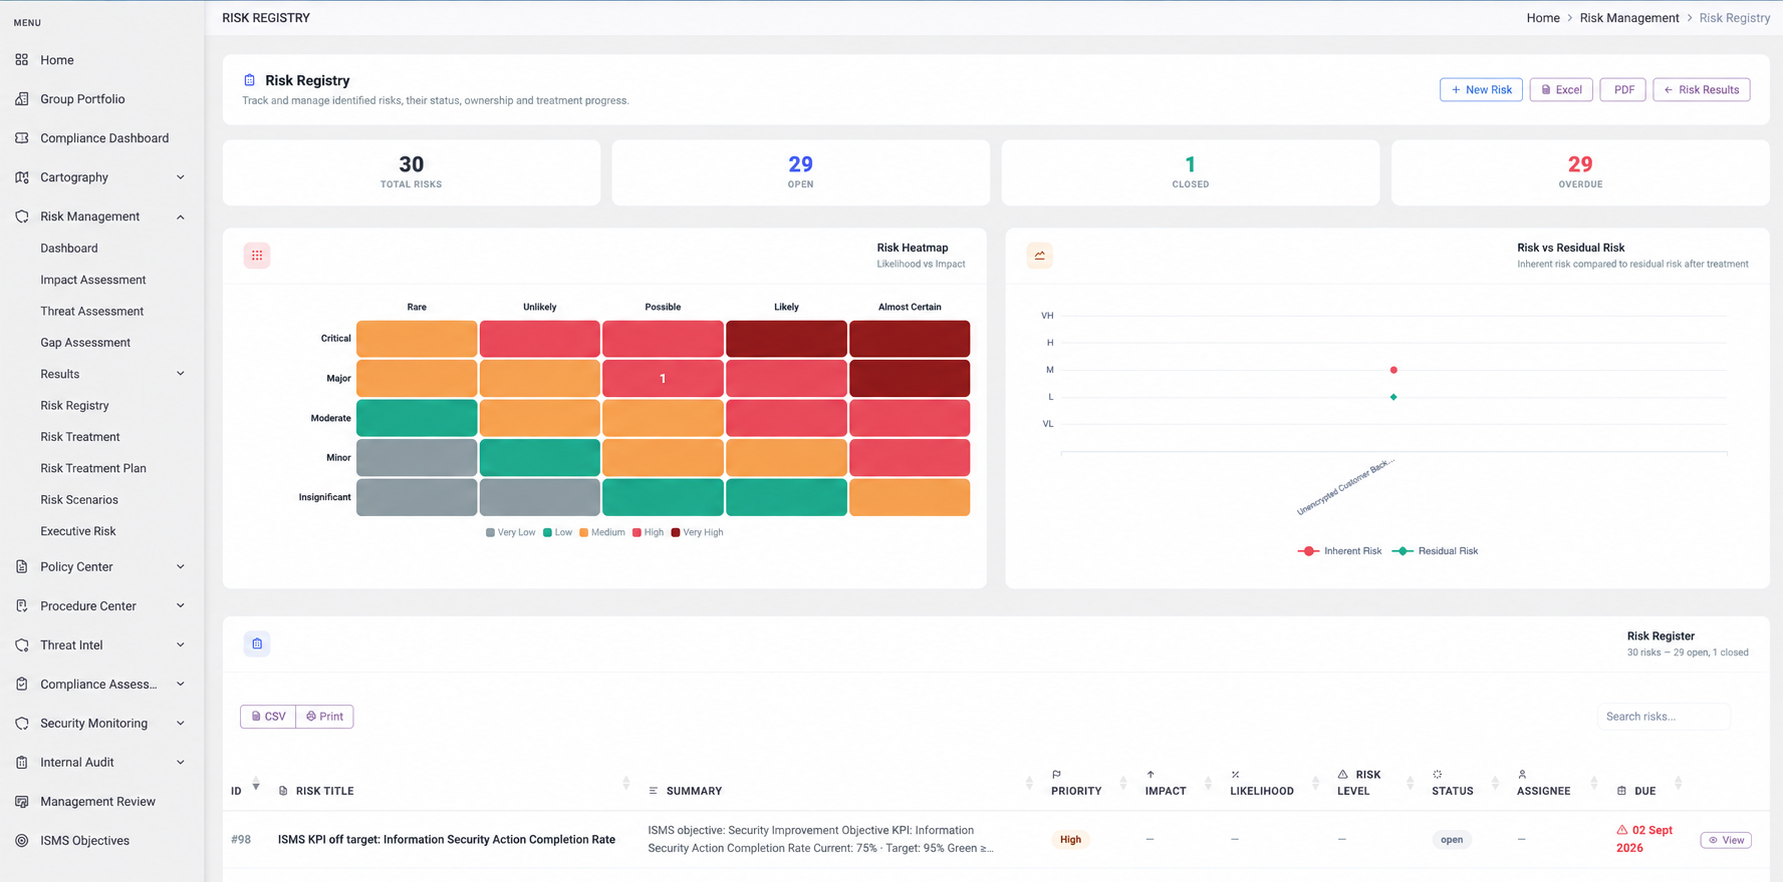
STORM includes DPIA and data-subject impact evaluation. Related concerns can be managed as custom risks with controls, treatment, owners and evidence.
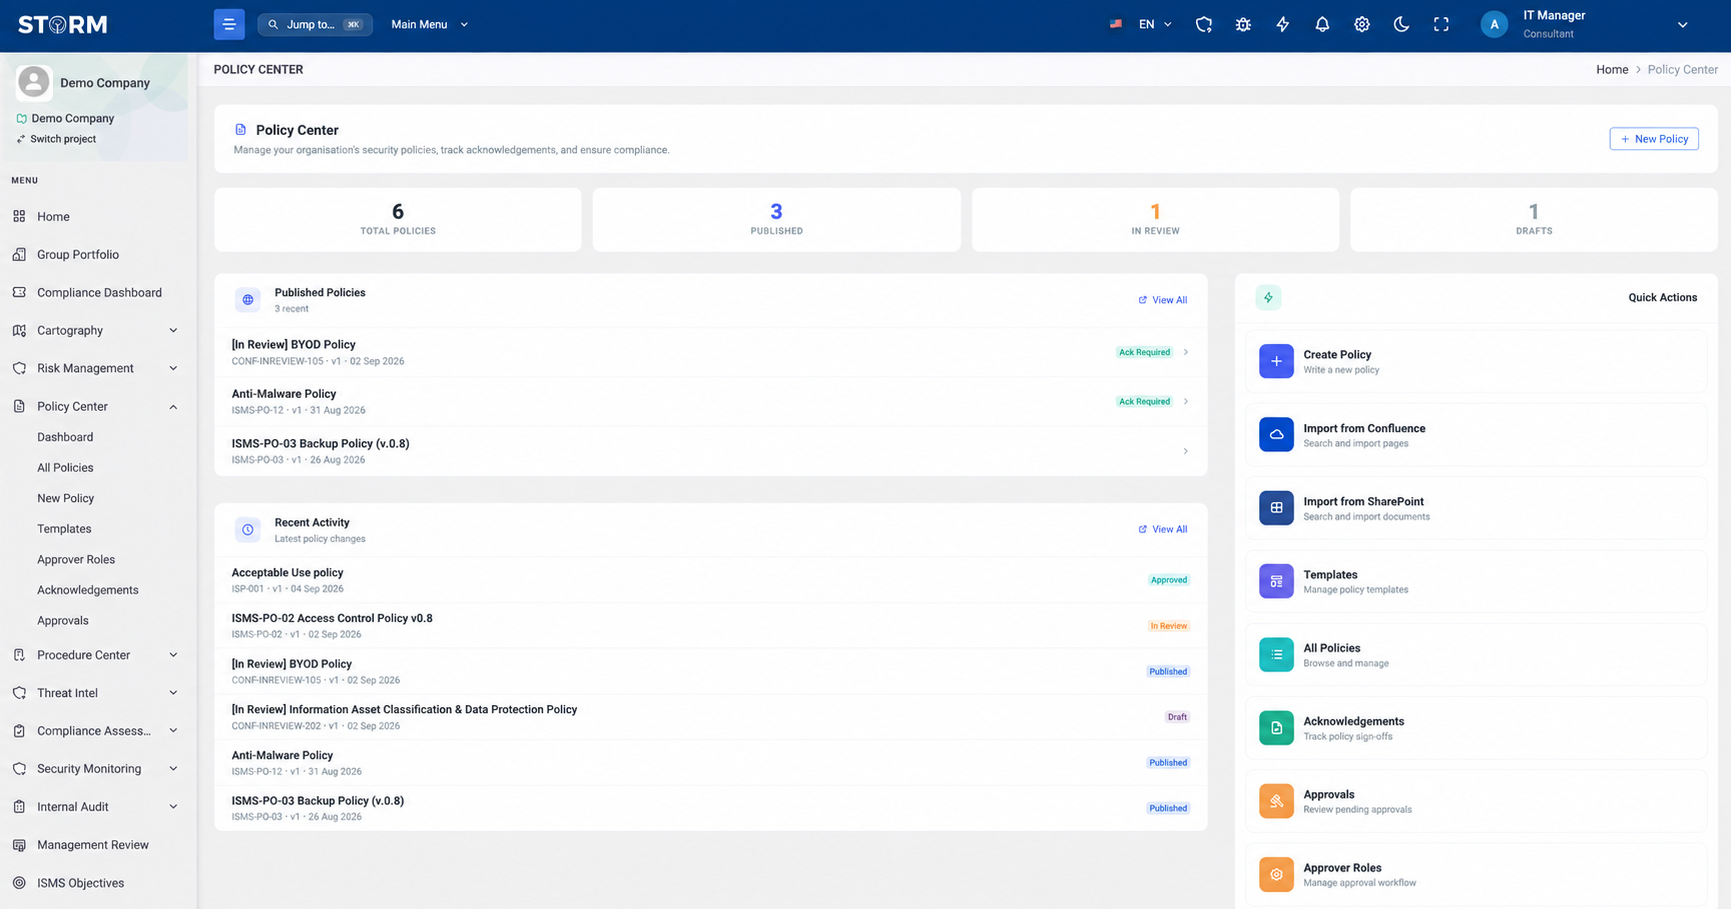
Use document ownership, workflow, review schedules and acknowledgement evidence to keep policies and procedures current and auditable.
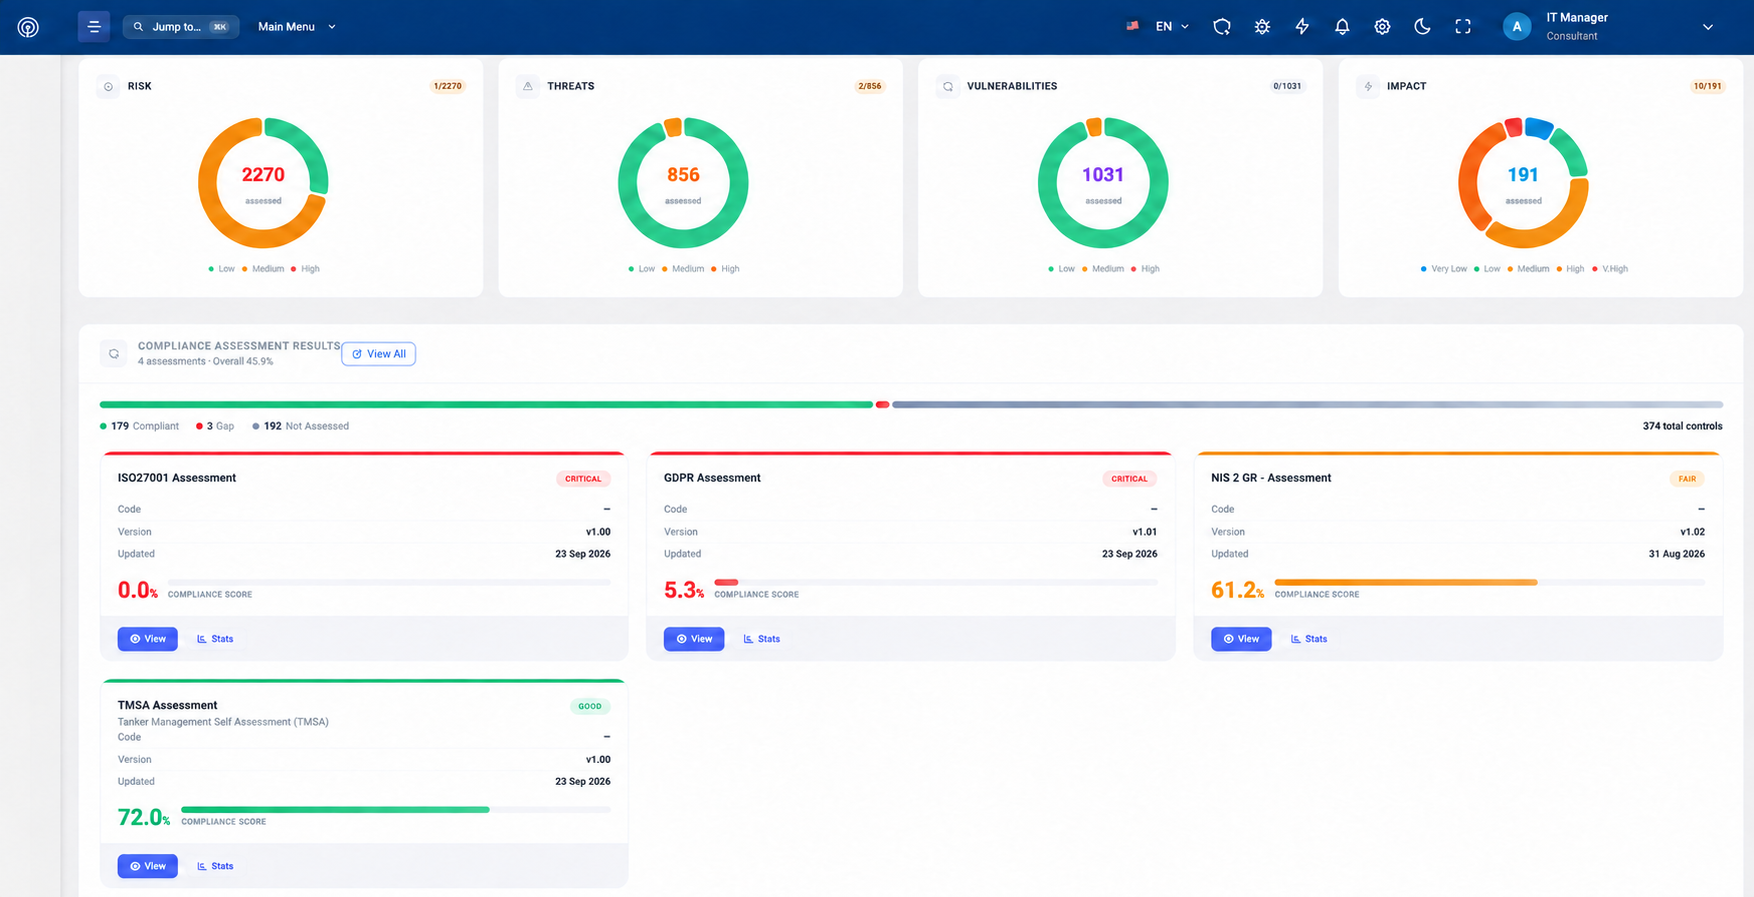
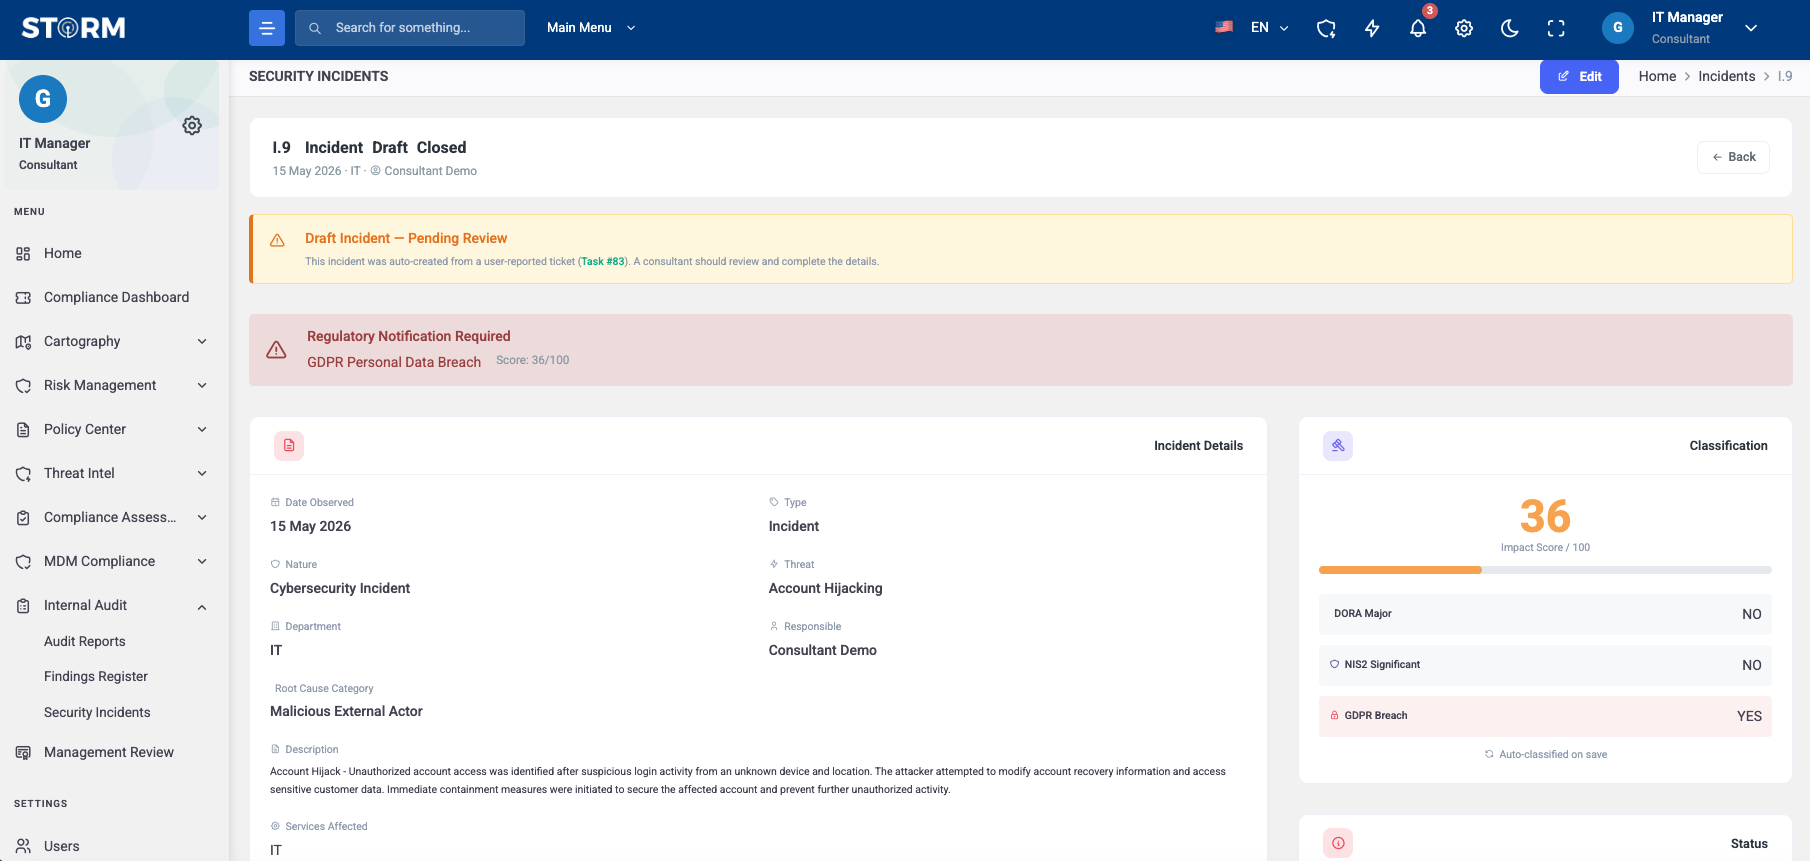
Configurable assessments, internal audits, incident records and management-review inputs support an evidence-led improvement cycle. PIMS-specific content still needs confirmation and configuration.
These implementation themes do not reproduce or replace the licensed ISO/IEC 27701:2025 requirements.
Define processing roles, relevant interested parties, legal context and PIMS boundaries.
Scope · roles · requirementsMaintain structured information about PII, activities, purposes, systems, flows and providers.
ROPA · mapping · inventoryEvaluate consequences for individuals and manage privacy risks through accountable decisions.
DPIA · risk · treatmentOrganise the policies, decisions and evidence relevant when determining processing purposes and means.
Purpose · accountability · evidenceDefine and assess the responsibilities that apply when PII is processed for another organisation.
Instruction · service · assuranceEvaluate external parties, collect evidence and monitor remediation around processing dependencies.
Due diligence · evidence · actionConnect privacy-relevant events to investigation, ownership, corrective action and review.
Incident · escalation · learningUse defined measures, audits and management decisions to drive continual improvement.
Monitor · audit · improveThe exact controller, processor and shared requirements must be determined from the licensed standard and the organisation's privacy context. STORM supports governance records; it does not replace qualified privacy or legal analysis.
A practical PIMS links requirements to records, accountable owners, evidence and management decisions.
Define roles, processing activities, PII, systems, suppliers and requirements.
Context · ROPA · mappingEvaluate privacy impacts, risks, provider posture and existing safeguards.
DPIA · risk · evidenceApprove policies, responsibilities, controls, procedures and action plans.
Policy · owners · controlsMonitor defined measures, assess implementation, audit and review performance.
Measures · audit · reviewCorrect gaps, respond to incidents and retain learning and decisions.
Actions · change · improvementThe 2025 standard, platform workflows, legal obligations and independent certification each have a distinct role.
Review your ROPA, data maps, DPIAs, controller and processor roles, privacy risks, policies, suppliers, incidents and audits—and identify which ISO/IEC 27701:2025 content still needs configuration.
ICT PROTECT, the company behind STORM GRC, holds internationally recognised certifications and independent assurance.
View all certificationsThe certifications and assurance reports shown here are held by ICT PROTECT and apply within their stated scope, which includes the STORM GRC platform.