STORM Platform · Third-Party Risk Management

Know which suppliers matter—and where to act.

Centralize supplier records, assess business impact and security posture, classify risk, collect supporting evidence and move material findings into accountable remediation.

STORM currently supports FortiRecon and BitSight integrations for external supplier-risk signals. Licensing and configuration are agreed during onboarding.

Supplier risk workspacePortfolio connected
0–8
Two dimensions. One decision view.

Business impact and security posture combine into a supplier score, tier and clear action path.

ImpactBusiness
PostureSecurity
TierPriority
EvidenceOversight
Supplier assessmentQuestionnaire · evidence · external signals
Assessed
Remediation planRisk · owner · follow-up action
Tracked
Supplier inventoryMaintain a centralized repository for third-party records.
Configurable methodEvaluate business impact and security posture with tailored criteria.
Signals + evidenceCombine questionnaires, attachments and external sources.
Tiered actionUse scores and tiers to guide monitoring or remediation.
From list to defensible oversight

One supplier view. Two risk dimensions. A clearer decision.

A questionnaire alone cannot explain how much a supplier matters or what external exposure changes the decision. STORM connects the supplier record with business impact, compliance responses, vulnerability exposure, disclosed breaches and supporting evidence so risk tiers are tied to visible inputs.

01 · REGISTER

Centralize suppliers

Maintain supplier details, categories, relationships and risk status in one repository.

02 · ASSESS

Measure impact

Apply configurable weighted business-impact criteria and assessment workflows.

03 · ENRICH

Add security posture

Bring together compliance, vulnerability and breach perspectives.

04 · ACT

Prioritize follow-up

Use risk tiers to guide monitoring, remediation planning or escalation.

Inside the platform

Supplier risk that stays connected to the evidence.

The workflow combines inventory, configurable assessment, external security context, tiering, reporting and remediation oversight.

01 · Supplier inventory

Give every third party a governed home.

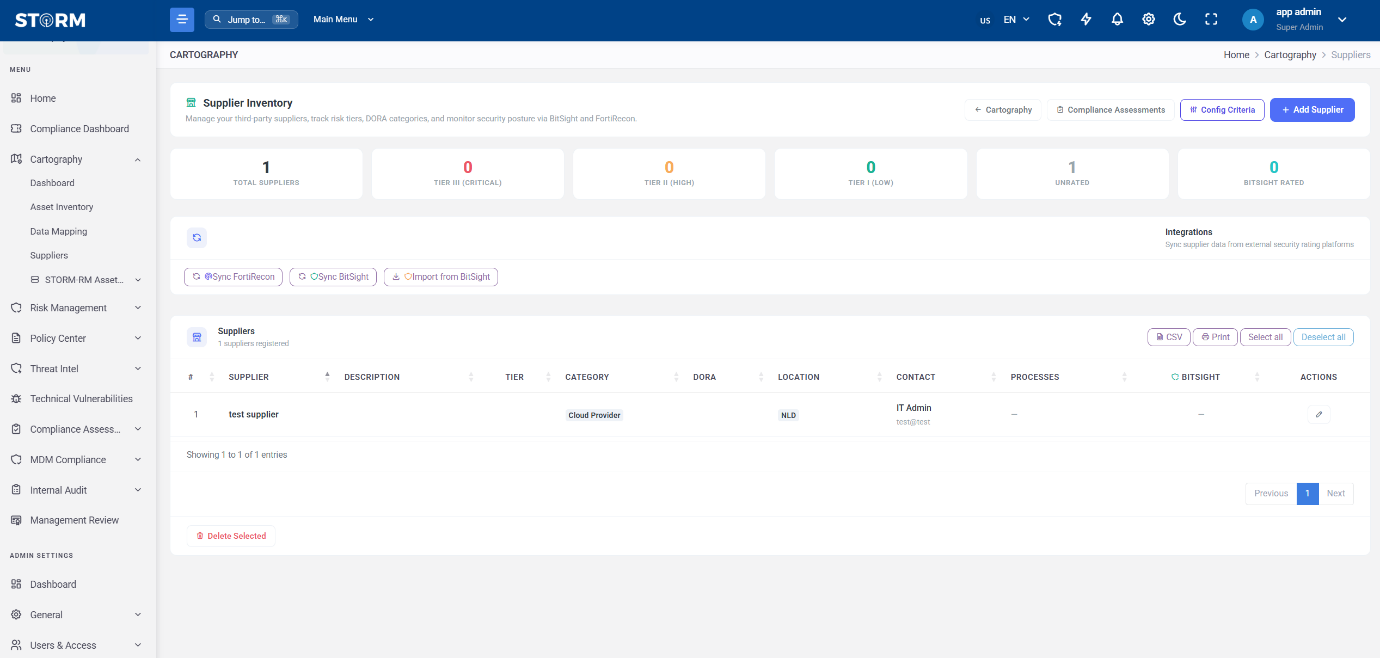
Maintain supplier details in a centralized repository, connect records with processes and services through Cartography, and keep categories, locations, contacts, tier status and available external-rating context visible.
  • Centralized supplier repository
  • Cartography process and service relationships
  • Portfolio-level tier and monitoring visibility
STORM Supplier Inventory showing portfolio metrics, integration actions and supplier records
Supplier InventorySTORM product interface · sample data
02 · Configurable risk methodology

Separate supplier importance from supplier security.

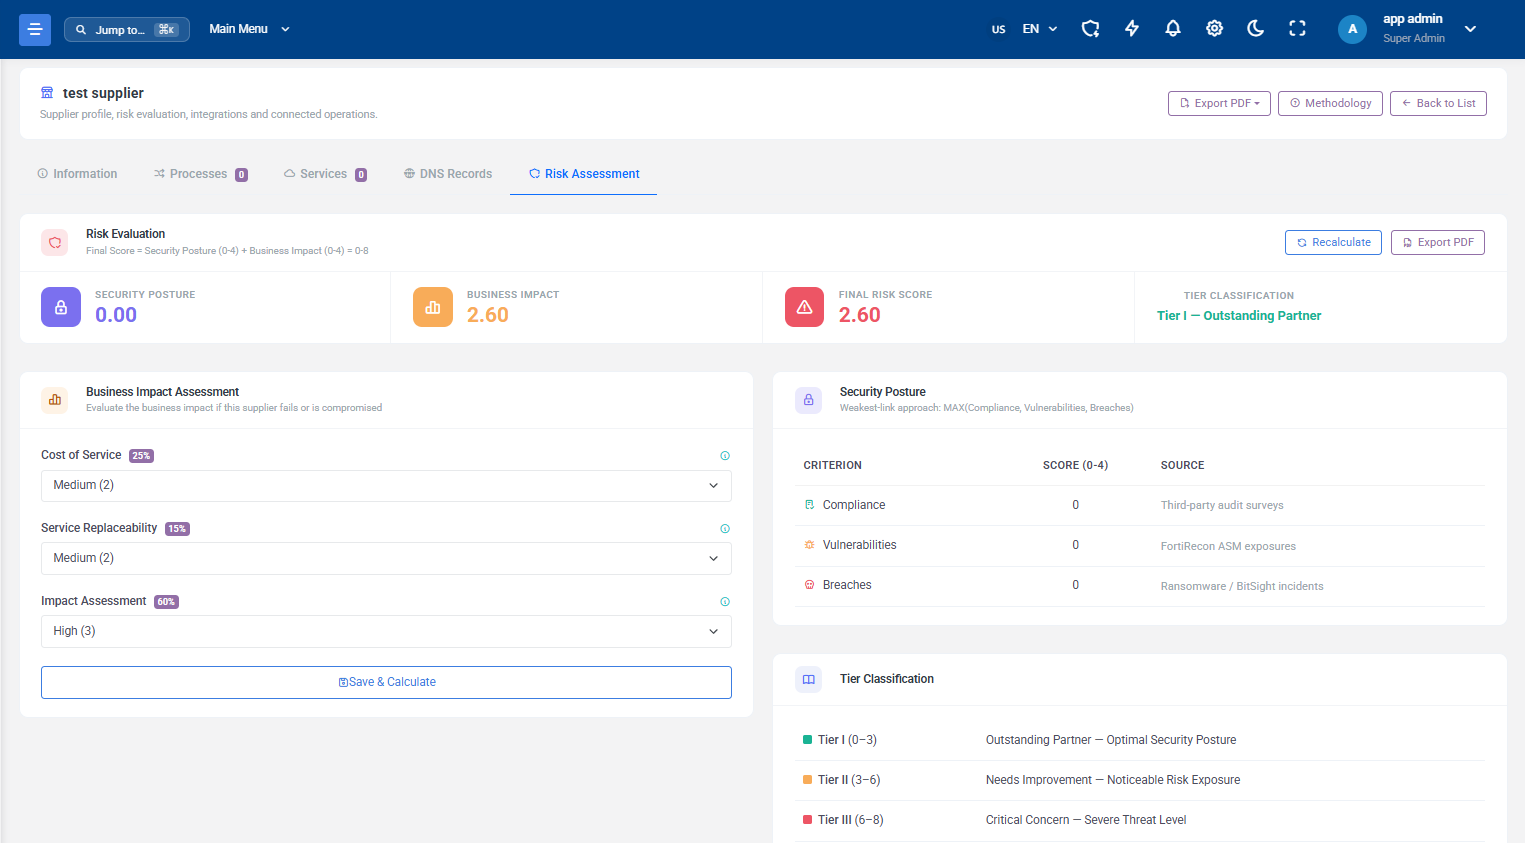
Evaluate each supplier across Business Impact and Security Posture. Business Impact uses configurable weighted criteria, while Security Posture applies a weakest-link approach across compliance survey results, vulnerability exposure and security breaches.
  • Configurable weighted business-impact criteria
  • Compliance, vulnerability and breach posture inputs
  • Combined final score from 0 to 8 with three tiers
STORM supplier risk assessment showing business impact, security posture, final score and tier classification
Supplier Risk AssessmentSTORM product interface · sample data
03 · Questionnaires and evidence

Let suppliers participate without losing oversight.

Use configurable supplier questionnaires and evaluation workflows. Through the Supplier Portal, suppliers can respond against selected frameworks, report implementation status and upload supporting evidence for individual controls.

  • Supplier self-assessment questionnaires
  • Framework-based implementation status
  • Control-level attachments and downloadable evidence
01
AssignSelect the assessment and supplier workflow
Invite
02
RespondRecord implementation status by control
Assess
03
SubstantiateUpload and review supporting evidence
Evidence
Supplier assessment workflowQuestionnaire → response → evidence
04 · External security context

Add outside-in signals to the supplier record.

Use the FortiRecon and BitSight integrations to retrieve external threat, breach or security-rating context for third-party monitoring and scoring. These signals inform the assessment; they do not replace the business-impact or compliance view.

  • FortiRecon threat, breach and supply-chain signals
  • BitSight external security ratings
  • Third-party risk monitoring dashboard
Built-in integrationsExternal signal → supplier context
05 · Tiering, reporting and remediation

Turn the result into an accountable next step.

Use the combined score to classify suppliers into three tiers and guide continuous monitoring, remediation planning or immediate action. Supplier risks can also be managed in the Risk Registry with owners, controls, treatment details, review dates and attachments.

  • Three-tier supplier classification
  • PDF and CSV supplier assessment exports
  • Linked risk ownership and remediation records
I
Tier IOutstanding Partner · continuous monitoring
0–3
II
Tier IINeeds Improvement · remediation planning
3–6
III
Tier IIICritical Concern · immediate action / exit strategy
6–8
Three-tier modelScore → tier → action path
From supplier record to action

Keep every risk decision connected and explainable.

STORM preserves the inputs behind each tier so teams can see why a supplier was prioritized and what follow-up the result requires.

01

Register

Supplier and relationship context

02

Assess

Business impact criteria

03

Collect

Questionnaire and evidence

04

Enrich

External security signals

05

Classify

Final score and risk tier

06

Act

Monitor or remediate

Scope and delivery

What Third-Party Risk Management includes.

Validate methodology settings, questionnaire content, integration prerequisites and remediation governance against the third-party programme you intend to run.

Included in STORM

  • Centralized supplier inventory and repository
  • Configurable assessment methodology and weighted business-impact criteria
  • Weakest-link security posture based on compliance, vulnerabilities and breaches
  • Combined 0–8 score and three supplier risk tiers
  • Questionnaires, evaluation workflows and supplier evidence
  • Monitoring dashboard with FortiRecon and BitSight integrations
  • Compliance Assessment and Cartography integration
  • PDF and CSV supplier risk reports with remediation oversight

Good to know

  • Criteria, weights and thresholds agreed at onboarding
  • Questionnaire frameworks and supplier access agreed at onboarding
  • FortiRecon and BitSight licences are arranged separately
  • Supplier exit and remediation are decided by your team
  • STORM provides evidence and workflow, not legal conclusions
Practical questions

Validate the model with a real critical supplier.

Bring one supplier, its service relationship, a completed questionnaire, representative external signals and an open remediation action to the walkthrough.

How does STORM calculate third-party risk?
The methodology combines Business Impact and Security Posture into a final score from 0 to 8. Business Impact uses configurable weighted criteria; Security Posture uses the weakest result across compliance surveys, vulnerability exposure and security breaches.
Which supplier tiers does STORM use?
Tier I covers scores 0–3 and supports continuous monitoring, Tier II covers 3–6 and points to remediation planning, and Tier III covers 6–8 and indicates immediate action or an exit strategy.
Can suppliers complete their own assessments?
Yes. Through the Supplier Portal, suppliers answer framework-based questionnaires, report implementation status and upload control-level evidence. Access and invitations are set up during onboarding.
Can supporting evidence be collected?
Yes. Suppliers can upload attachments for individual controls, and the submitted evidence can be downloaded by suppliers and consultants within the assessment workflow.
Which external integrations support supplier risk?
FortiRecon provides external threat and breach intelligence, including supply-chain risk signals. BitSight provides external security ratings used in supplier security-posture evaluation and scoring.
Does an external rating determine the full supplier score?
No. The method also considers business impact, compliance surveys, vulnerability exposures and security breaches.
Can supplier risks be tracked beyond the assessment?
Yes. The Risk Registry supports risks derived from TPRM, including likelihood, impact, controls, mitigation plans, treatment strategy, ownership, review dates and attachments.
Which TPRM report formats are available?
Supplier risk assessment reports can be exported as PDF and CSV.

Bring one critical supplier and one open concern.

Validate the supplier record, business-impact criteria, questionnaire evidence, external security context, tier result and remediation path against your operating model.

Book a STORM demo
Certifications

ICT PROTECT, the company behind STORM GRC, holds internationally recognised certifications and independent assurance.

View all certifications
  • CERTIFIED ISO 27001
  • CERTIFIED ISO 22301
  • CERTIFIED ISO 9001
  • CERTIFIED CYBER ESSENTIALS
  • CERTIFIED CYBER ESSENTIALS PLUS
  • ASSURANCE ISAE 3000 TYPE II

The certifications and assurance reports shown here are held by ICT PROTECT and apply within their stated scope, which includes the STORM GRC platform.